Keep your methodology
Your risk and control matrix, your processes, your sampling criteria and your own formats. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools
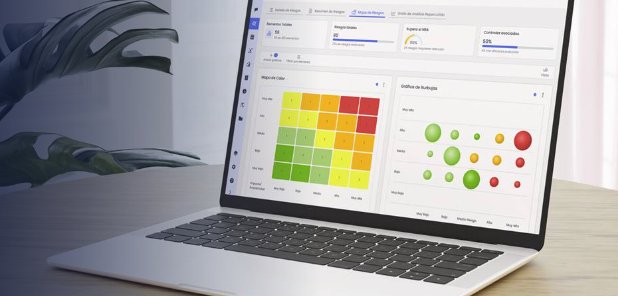
Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Risk and control matrix, walkthroughs, testing, deficiencies and sub-certifications in one place. From the annual assessment of internal control (Section 404) to the certification of every report (Section 302).
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
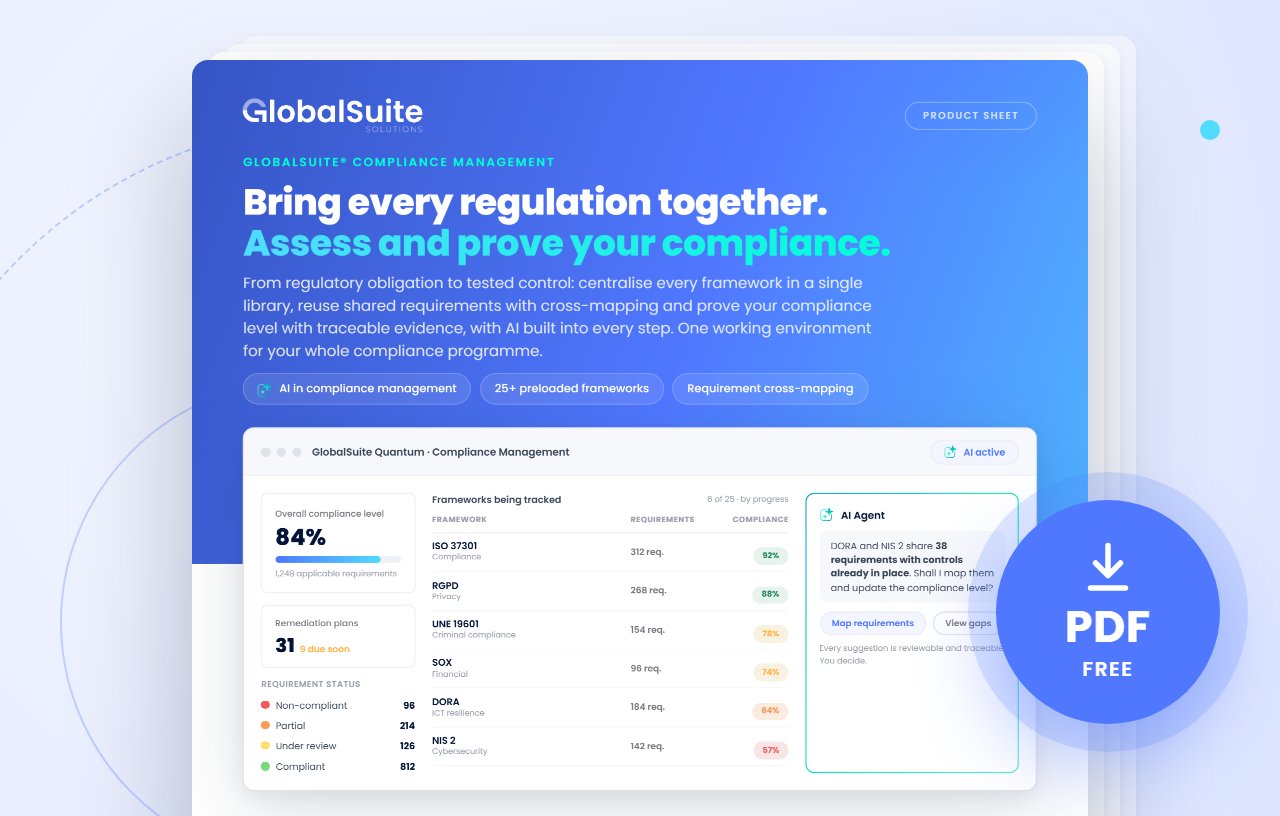
What the law requires, what you've already done and what's missing, in a single platform. Screens with sample data.
Each section of the Act with its status and level of compliance for the year, with Section 404 in view.
Each section of the Act with its status and level of compliance for the year, with Section 404 in view.
Each process in its tree, with its sub-processes, the systems it uses and who is responsible for each step.
Operating effectiveness testing for each process in the audit tool: controls tested, risks reviewed and exceptions.
Pick a risk in an in-scope system and the AI suggests IT general controls aligned with COSO. Add them to the plan and the residual risk is recalculated.
Each quarter the sub-certification follows its sign-off workflow: control owners, area directors and, last, senior management.
The Power BI dashboard for management and the audit committee, with up-to-date data.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your risk and control matrix, your processes, your sampling criteria and your own formats. You start with what you already have.
Risk and control matrix, tests with their evidence and a deficiency report for the audit committee, up to date and ready to download.
Before every close, the agent goes through the control matrix, finds the controls that are untested or lack evidence and drafts the plan. You just validate it.
The processes, financial reporting risks and controls you test for SOX are the foundation of SCIIF, the Spanish ICFR framework, and fit into your risk and compliance management. In GlobalSuite® you do it once and it works for all of them.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI
Monitoring
Vulnerabilities
Data lake
And the module is part of the GRC platform. The processes, risks and controls you set up for SOX are the same ones used by SCIIF, internal audit and the rest of the group's obligations.
If you already work on SCIIF or another ICFR framework, much of the control matrix is already done.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Rail transport · 14,000+ employees
As we rolled out risk management and compliance processes, and given the size of the company and the range of its activities, we needed software that would make risk management more effective and efficient.
Diego Molero AlonsoDirector of Internal Audit, Compliance and Business Risk · Renfe
Integration of compliance regulations, the catalog of standards, and risks in an integrated and coherent manner.
From day one, the onboarding process was excellent, allowing us to understand the platform really fast, thanks to their top-notch support team. The UI is clean and intuitive, making it easy to use for everyone.
It reduces tool fragmentation and centralizes all evidence, documentation, controls, and assessments in one place.
Shall we look at it with your risks and your methodology?
Request a demoCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.